Professional Skills & Expertise
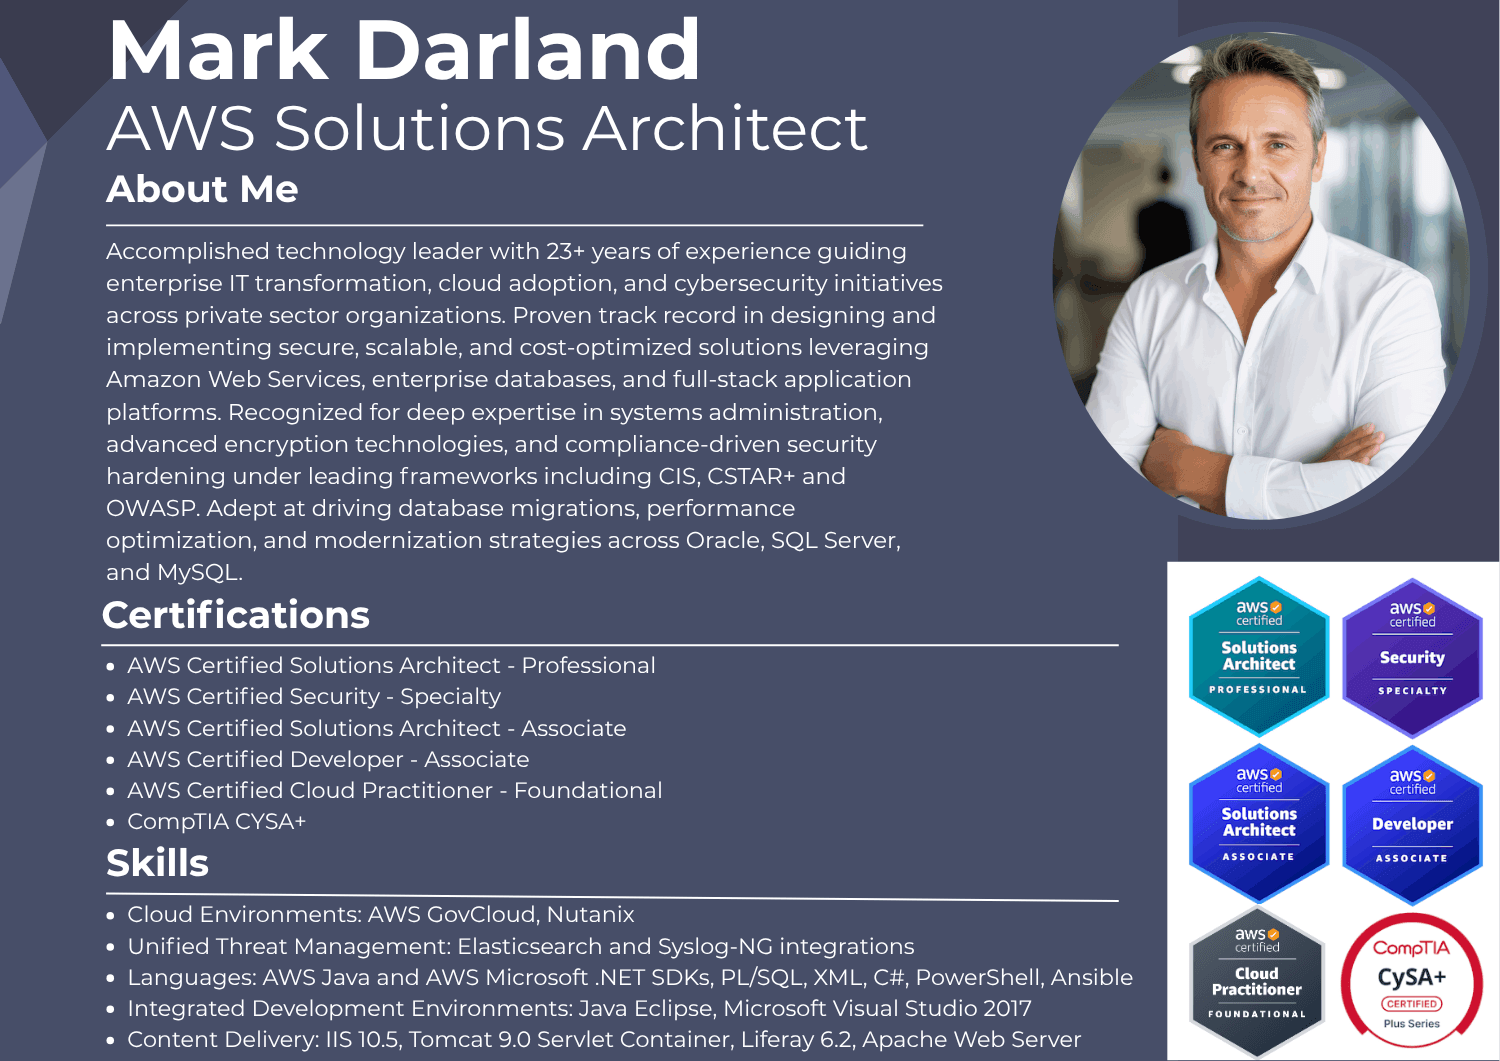
Over 23 years of experience in information technology, with specialized focus on cybersecurity, secure coding practices, and enterprise security architecture. Committed to implementing robust security measures that protect critical infrastructure while enabling business objectives.
Security Standards & Frameworks
- OWASP Top 10 & Secure Coding Standards
- ISO 27001/27002 Information Security
- NIST Cybersecurity Framework
- CIS Controls Implementation
- PCI DSS Compliance
Application Security
- Secure Code Review & Analysis
- Static & Dynamic Application Security Testing (SAST/DAST)
- Threat Modeling & Risk Assessment
- Security Architecture Design
- Vulnerability Management
Network & Infrastructure Security
- Firewall Configuration & Management
- Intrusion Detection/Prevention Systems (IDS/IPS)
- Border Gateway Protocol (BGP) Security
- Network Access Control (NAC)
- Security Information and Event Management (SIEM)
Cloud Security
- Cloud Security Posture Management (CSPM)
- AWS Security Best Practices
- Azure Security Center
- Data Loss Prevention (DLP)
- Identity & Access Management (IAM)
Authentication & Authorization
- Kerberos Authentication
- Multi-Factor Authentication (MFA)
- Single Sign-On (SSO) Solutions
- OAuth & OpenID Connect
- Role-Based Access Control (RBAC)
Security Operations
- Incident Response & Forensics
- Security Monitoring & Alerting
- Penetration Testing Coordination
- Security Policy Development
- Security Awareness Training
Career Overview
Throughout my career, I have worked with organizations of various sizes to establish and maintain comprehensive security programs. My approach emphasizes practical, risk-based security that aligns with business goals while maintaining strong defensive postures.
I have led initiatives in secure software development lifecycle implementation, security architecture reviews, and incident response planning. My expertise in OWASP secure coding standards has been instrumental in helping development teams build security into applications from the ground up, reducing vulnerabilities and strengthening overall security posture.